Online Reporter
Business Reporter
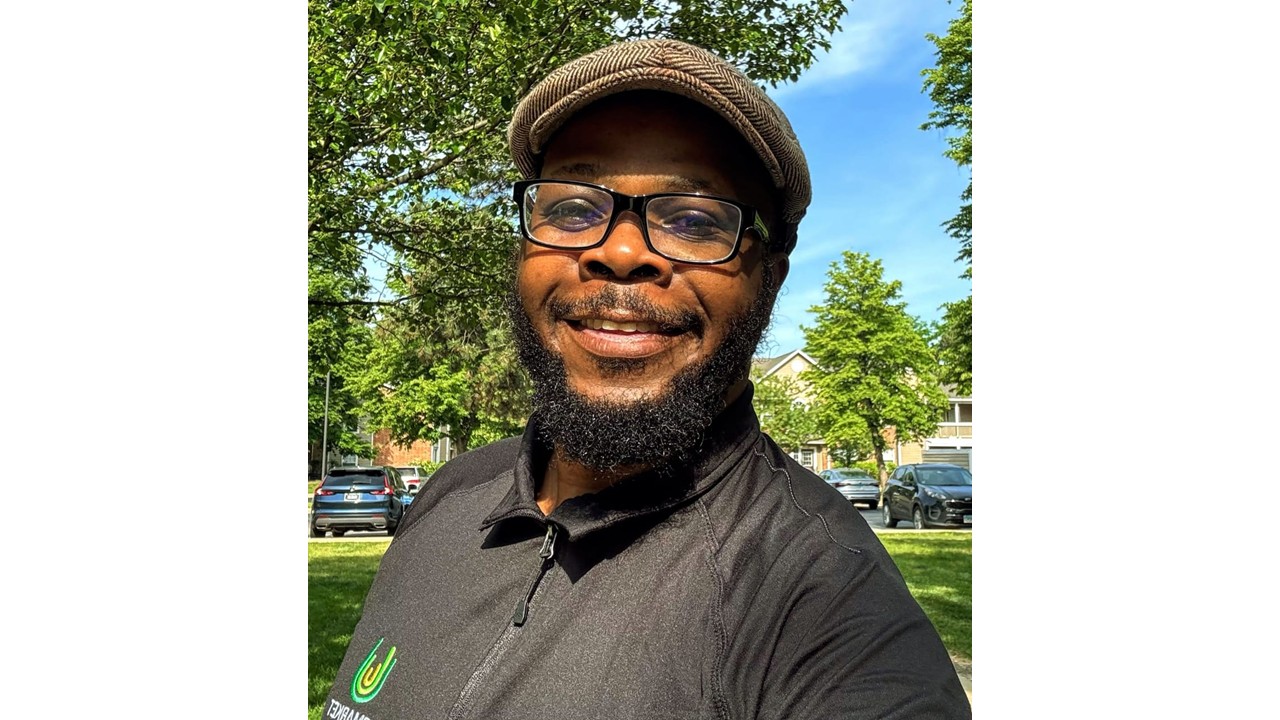
ARTIFICIAL intelligence (AI) is rapidly transforming governments, businesses and societies, but its benefits could be undermined by weak data governance, inadequate cybersecurity controls and gaps in cyber law, cybersecurity and regulatory compliance expert Tafadzwa Mungwadzi has warned.
Mungwadzi, who has advised governments and corporates across several countries on cybersecurity, cyber law, data governance and regulatory compliance, said organisations adopting AI must treat data governance and cybersecurity as fundamental requirements rather than mere administrative or compliance exercises.
As organisations increasingly deploy AI to support decision-making, automate processes and analyse vast amounts of information, concerns over data quality, privacy, accountability, cybersecurity and the potential misuse of AI systems are growing.

“Artificial intelligence is only as safe as the data ecosystems that support it. Without strong, enforceable data governance frameworks, AI can amplify existing vulnerabilities, accelerate misinformation and expose organisations to unprecedented cyber risks. We need governance that is proactive, not reactive,” said Mungwadzi.
His comments come as organisations worldwide grapple with the security implications of increasingly sophisticated AI systems, including generative AI and autonomous AI agents.
According to Mungwadzi, the quality and governance of underlying data are critical in determining whether AI systems can be trusted.
“AI systems must be built on foundations of transparency, accountability and rigorous data quality controls. If we fail to govern how data is collected, stored and used, we risk creating AI models that are biased, insecure and easily manipulated. Good data governance is not a ‘nice to have’, but a critical security requirement,” he said.
The cybersecurity expert said organisations should establish clear controls over the entire data lifecycle, from collection and classification to storage, access, processing, sharing and eventual disposal.
He said this was particularly important as organisations integrate AI into sensitive sectors such as financial services, healthcare, government services, critical infrastructure and national security.
Cyber law must keep pace with AI
Mungwadzi said the legal and regulatory environment surrounding emerging technologies must evolve as AI becomes increasingly embedded in society.
Having advised on cyber law and regulatory compliance, he said organisations and governments needed to consider not only whether an AI system worked, but also whether its deployment complied with applicable legal, privacy, cybersecurity and data protection requirements.
The rapid development of AI, he said, was raising new questions around accountability, data ownership, privacy, automated decision-making, intellectual property and responsibility when AI systems cause harm.
This makes the intersection of AI, cybersecurity, data governance and cyber law increasingly important for policymakers and corporate leaders.
AI risks extend beyond government
While governments have an important role to play in establishing laws, regulations and national cybersecurity standards, Mungwadzi said responsibility for AI security could not rest solely with regulators.
“Managing AI risks cannot be left to government alone. Corporates must invest in responsible AI practices and individuals need to understand how their digital behaviour shapes the broader risk landscape. AI safety is a shared responsibility — every stakeholder has a role to play,” he said.
He said businesses should incorporate cybersecurity, data governance and legal considerations into AI projects from the design stage, instead of attempting to address risks after systems had already been deployed.
This includes establishing appropriate access controls, monitoring data quality, maintaining data lineage, protecting sensitive information and ensuring that organisations understand what data is being used to train or operate AI systems.
Mungwadzi also warned that employees and consumers had an important role to play in the emerging AI security environment.
The rapid adoption of AI-powered applications means individuals are increasingly interacting with systems capable of collecting, processing and generating large quantities of information.
Poor digital practices, he said, could contribute to wider organisational and societal risks.
Collective action needed
Mungwadzi said the scale of AI’s impact meant that effective security would require cooperation among governments, businesses, technology providers, legal and cybersecurity professionals, and ordinary citizens.
“AI touches every part of society, which means safeguarding it requires collective action. Governments can set the regulatory baseline, but businesses must operationalise those standards, and citizens must stay informed and vigilant. The future of AI security depends on all of us,” he said.
His remarks highlight the growing convergence of artificial intelligence, cybersecurity, cyber law, data governance and regulatory compliance.
For organisations, this means deploying an AI system should no longer be viewed simply as a technology project. It is increasingly a governance, legal and risk-management exercise requiring senior leadership oversight and clearly defined accountability.
Strong data governance can help organisations build confidence in the information used by AI systems, identify inappropriate or unauthorised data use, improve data quality and establish accountability for decisions made with the assistance of AI.
For governments, the challenge is equally significant. Regulators must balance innovation with the protection of citizens, businesses and national interests while ensuring that emerging technologies are developed and deployed responsibly.
Mungwadzi’s position is that regulation, technology, cybersecurity and organisational practices must evolve together.
As African countries accelerate their digital transformation and explore AI applications across the public and private sectors, establishing strong data governance frameworks will be essential to ensuring that technological progress does not create new and avoidable risks.
The message from Mungwadzi is clear: AI innovation cannot be separated from responsible data management, cybersecurity, appropriate cyber law and effective regulatory frameworks.
Organisations seeking to benefit from AI while maintaining public trust will need to ensure that the data underpinning their systems is accurate, properly governed, secure and used responsibly.
In an increasingly AI-driven economy, strong data governance may prove to be not merely a compliance obligation, but a vital foundation for digital security, legal accountability and public trust.